For nonprofits, foundations, and growing businesses

Protect your business.Power your impact.

Know where you're exposed. Fix what matters. Give leadership a clear plan and your people the skills to use AI with confidence.

30-minute discovery call. No obligation.

What does your business need next?

Start with your priority. Combine services as needs change.

01 · Security assessment

Know what to fix first.

We review your Microsoft 365 identity and access settings using read-only access, then show the evidence and what to fix first.

What you receive

  • Evidence-backed findings report
  • Prioritized remediation runbook
  • Executive scorecard
See the assessment scope

Assessment identifies the gaps. Remediation turns the priorities into approved, verified fixes.

See how remediation builds on this

Independent · Principal-led

Executive perspective.
Practical delivery.

About Mount Xion

SBA-certified SDVOSB

Service-Disabled Veteran-Owned Small Business. Based in San Antonio, working with organizations nationwide.

Experience at enterprise scale

Our principal led IT and cybersecurity for a $1B+ organization, bringing strategy, security, vendors, and budget into one plan.

See what you receive

From security findings
to a plan you can use.

Evidence for your technical team. Clear priorities for leadership.

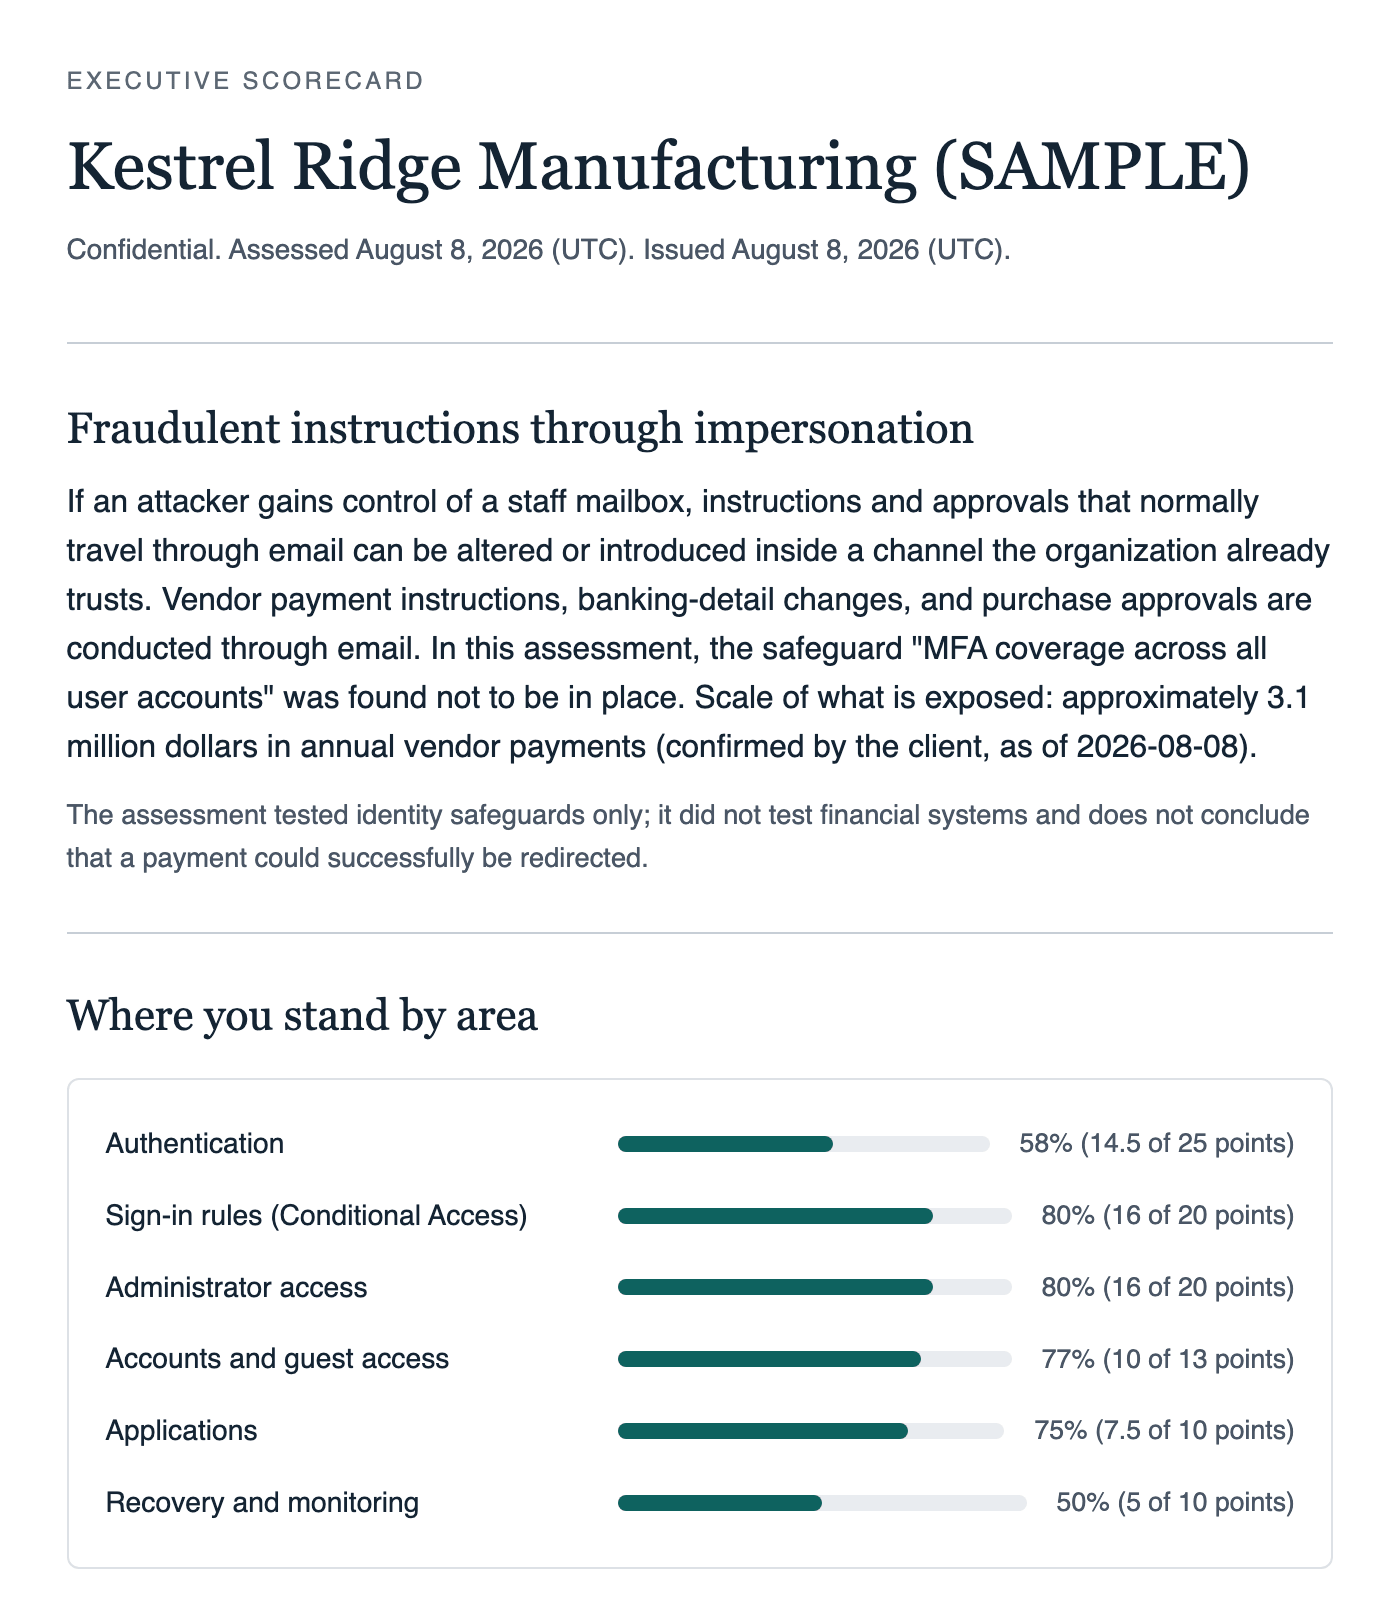
Sample · Fictional dataExcerpt from a sample executive scorecard for Kestrel Ridge Manufacturing (SAMPLE), an invented company: a business scenario, fraudulent instructions through impersonation, connects the missing MFA safeguard to about 3.1 million dollars in annual vendor payments (a fictional figure), then six safeguard areas scored as bars, from Authentication at 58 percent to Recovery and monitoring at 50 percent. The same content is available as text below.
A sample executive scorecard, using fictional company data. It shows security gaps, what they expose, and an ordered action plan. One finding, incomplete multifactor sign-in protection, is connected to about $3.1 million a year in vendor payments whose instructions travel through email (a fictional figure).

What an assessment hands over.

Every finding cites its evidence, every priority has a next action, and leadership gets a readout it can take to the board.

Evidence-backed findingsEach safeguard checked against preserved evidence, with the file cited. No evidence, no credit.
Prioritized remediation planOrdered steps for your team or IT provider, with lockout risks and dependencies called out.
Executive scorecard and readoutThe picture in plain language, connected to what the organization depends on, plus a 90-minute readout with your team.

Clear scope, named deliverables, and a fixed fee, all set before the review begins.

Read the sample scorecard

An excerpt from the executive scorecard prepared for Kestrel Ridge Manufacturing (SAMPLE), an invented company, assessed August 8, 2026: the same scenario and bars as the scorecard image, plus the plan's first priorities, as text.

Business scenarios connected to current findings

Fraudulent instructions through impersonation. If an attacker gains control of a staff mailbox, instructions and approvals that normally travel through email can be altered or introduced inside a channel the organization already trusts. Vendor payment instructions, banking-detail changes, and purchase approvals are conducted through email. In this assessment, the safeguard "MFA coverage across all user accounts" was found not to be in place. Scale of what is exposed: approximately 3.1 million dollars in annual vendor payments (confirmed by the client, as of 2026-08-08; a fictional figure).

The assessment tested identity safeguards only; it did not test financial systems and does not conclude that a payment could successfully be redirected.

Where you stand by area

  • Authentication58% (14.5 of 25 points)
  • Sign-in rules (Conditional Access)80% (16 of 20 points)
  • Administrator access80% (16 of 20 points)
  • Accounts and guest access77% (10 of 13 points)
  • Applications75% (7.5 of 10 points)
  • Recovery and monitoring50% (5 of 10 points)

What to do first

The issued remediation plan sequences the work so recovery safeguards land before any change that could lock anyone out. Its first priorities are:

  1. Emergency-access accounts exist, are protected, and are tested
  2. MFA coverage across all user accounts
  3. Authentication methods policy is managed and weak methods are disabled
  4. Conditional Access policies specifically protect administrator sign-ins
  5. Administrators use separate accounts for privileged work
Prepared for Kestrel Ridge Manufacturing (SAMPLE), an invented company. Scores describe safeguard coverage; they are not a compliance certification.

Read the sample finding

MFA coverage across all user accounts

Not in place
What the evidence shows
The preserved evidence shows that multifactor sign-in is not in place across all user accounts. The evidence file is cited in the finding.
Why it matters
If an attacker gains control of a staff mailbox, instructions and approvals that normally travel through email can be altered or introduced inside a channel the organization already trusts.
Next action
Step 4 of the issued plan: run the tenant-wide user MFA registration campaign. Depends on: none. The safeguard can be verified during the next assessment.

Prepared for Kestrel Ridge Manufacturing (SAMPLE), an invented company. No client is named or implied.

Our approach

From priorities to practical progress.

Define

Agree on the scope, outcomes, and responsibilities.

Deliver

Carry out the work with your organization.

Verify

Document the outcome and the next steps.

For government buyers and primes

A focused partner for security and readiness work.

Microsoft 365 security assessment and hardening, CMMC readiness, and AI governance as a subcontractor or teaming partner.

Explore readiness and teaming

SBA-certified SDVOSB · Texas HUB

Readiness, with a clear plan

Review all 110 NIST SP 800-171 Rev. 2 controls, identify evidence gaps, and prioritize the work before a certification assessment.

Defined work alongside your team

Scoped support for primes, agencies, and Texas DIR contract holders, with responsibilities and deliverables agreed before work begins.

Experience behind the work

Leadership put into practice.

Examples from our principal's prior organizational leadership, with the scope, decisions, and outcomes behind each engagement.

Security assessmentA security program built from zero evidence.21 findings, four remediation tiers AI adoptionAn entire staff brought into governed enterprise AI.100% onboarded, 98% daily use Cloud modernizationA $1B+ organization moved fully to the cloud.Fully cloud, every device managed Financial stewardshipDelivered under budget in a deficit year.~$24K under plan, $15K+ savings
Where we work

Based in San Antonio. Working across Texas and nationwide.

Every engagement runs on site or virtually, across Texas and anywhere in the United States. Most work runs remotely, with on-site readouts, workshops, and training arranged wherever they genuinely help.

San Antonio

Home base, minutes from JBSA and the VA's South Texas market. On-site readouts, workshops, and training sessions across the metro area, from the Medical Center to New Braunfels.

Austin

State agencies, universities, and the growing organizations around them. On-site delivery is a short drive up I-35, with the review work itself done remotely.

Houston

Nonprofits, foundations, and growing businesses running on Microsoft 365. On site for readouts and training sessions, remote for the assessment itself.

Dallas-Fort Worth

The same engagements, delivered on site across the Metroplex or virtually, with the readout in the room when leadership wants it there.

Anywhere in the US, on site or virtual

Assessments run read-only and remote, so a tenant in El Paso, Lubbock, or the Rio Grande Valley gets the same evidence and the same readout as one down the road, and so does an organization in any other state. On-site readouts, workshops, and training travel wherever they are wanted, in Texas or across the United States.

Texas HUB and VetHUB

Texas HUB certified through the Comptroller's veteran program (VetHUB), so state agencies, universities, and DIR contract holders can count Mount Xion toward HUB subcontracting plans. SBA-certified SDVOSB and VOSB for federal set-asides.

Straight answers, up front.

Do you replace our MSP or IT staff?

No. Mount Xion is independent and assessment-first. We work alongside your internal team or your MSP; we don't replace either one.

How do you charge?

Two models: a fixed-scope project (like the security posture assessment) or a monthly fractional retainer. Either way, you see the scope and the price before any work starts: no hourly surprises and no upsell quota.

Can you review our software licenses and vendor contracts?

Yes. We review licenses, subscriptions, and vendor and MSP contracts before they renew, right-size what is over-bought, consolidate tools that overlap, and check billing against contract pricing. It runs inside a fractional retainer or as a fixed-fee project on its own.

What does a fractional engagement actually look like?

A standing monthly rhythm: leadership check-ins, vendor and project oversight, security review, and a board-ready report. You get a named executive who owns technology outcomes, for a fraction of an executive salary.

What happens after an assessment?

The plan is yours, and it is written to be handed off. Your existing team or your MSP can execute it task by task; Mount Xion can also stay on in a fractional role to see it through. Either path is a good outcome.

We're small. Is this overkill?

Small organizations face the same threats as large ones, with less room to absorb a loss. Engagements are sized to the organization: sometimes that's a one-time assessment and a prioritized plan, nothing more.

Do you only work in San Antonio?

No. Mount Xion is based in San Antonio and works across Texas and nationwide, on site or virtually. Most work runs remotely; on-site readouts, workshops, and training are arranged wherever they genuinely help, in Austin, Houston, Dallas-Fort Worth, or any other state.

What's your next technology priority?

Let's build a clear path forward.

30 minutes. No obligation.Bring a board question, a security worry, or an AI mandate, in whatever shape it is in.
What we coverYour organization, your priorities, and which service fits, if any.
What you leave withA clear next step. If there is a fit, we agree what needs scoping and prepare a proposal with scope, deliverables, and fees for your review.

Book a discovery call

Selected topic: General discussion

Prefer email? [email protected] · (210) 729-0079

Every engagement starts with clear priorities, a defined scope, and a fixed price.